Buy firmengründung.eu ?
We are moving the project
firmengründung.eu .
Are you interested in purchasing the domain
firmengründung.eu ?
domain@kv-gmbh.de · 0541-91531010
Buy firmengründung.eu ?
Why does the PC crash during startup? TPM 2.0
The PC may crash during startup due to issues with the Trusted Platform Module (TPM) 2.0. TPM 2.0 is a hardware-based security feature that stores encryption keys, passwords, and digital certificates. If there are compatibility issues with the TPM 2.0 chip or its firmware, it can cause the PC to crash during startup. Additionally, if the TPM 2.0 is not properly initialized or configured, it can also lead to startup crashes. It is important to ensure that the PC's hardware and firmware are compatible with TPM 2.0 and that it is properly set up to avoid startup crashes. **
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
Similar search terms for Tpm
Top-Angebote
Products related to Tpm:
-
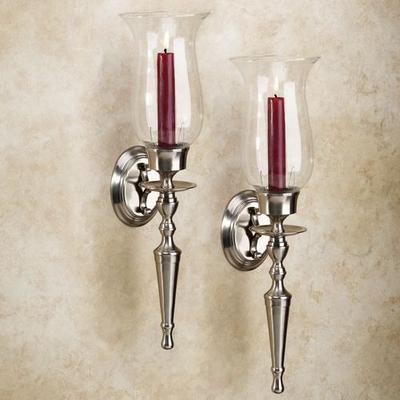
Flythe Consulting Arika Wall Sconce Pair, Pair, Satin NickelThe Arika Wall Sconce Pair is an adaptation of old-fashioned light fixtures, with an appealing design that will complement modern decor. The lacquered solid brass sconces have 4.75 dia.x7 H clear glass hurricanes that will protect your standard...179,00 $*Shipping: 22,95 $Secure redirect to the provider
-
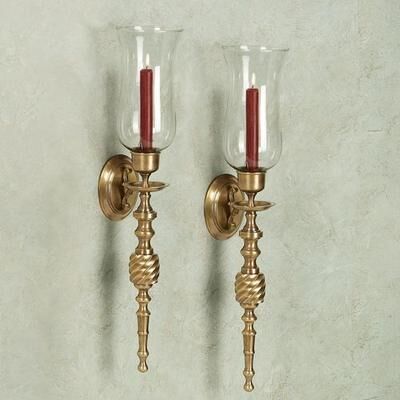
Flythe Consulting Jonetia Hurricane Wall Sconce Pair Satin Brass, Pair, Satin BrassThe Jonetia Satin Brass Hurricane Wall Sconce Pair proudly displays grandeur on your walls. These hand-forged, solid brass sconces feature a diamond design and fleur-de-lis motif. Sconces have a lacquered, satin brass finish that is done by hand. A...229,00 $*Shipping: 32,06 $Secure redirect to the provider
-
Picador Bad Blood: Secrets and Lies in a Silicon Valley Startup by John Carreyrou - Paperback - True Crime Business Book - Theranos Scandal ExposéBad Blood is John Carreyrou's Pulitzer Prize-winning investigation into Theranos, the blood-testing startup once valued at over $9 billion before collapsing into one of the biggest corporate frauds in American history. This gripping true-crime business narrative follows founder Elizabeth Holmes from Silicon Valley darling to disgraced fraudster, exposing the culture of secrecy, intimidation, and deception that hid a technology which simply didn't work — with devastating consequences for real patients. In 2014, Elizabeth Holmes was celebrated as the next Steve Jobs: a charismatic Stanford dropout whose startup promised to revolutionise healthcare with a single drop of blood. Backed by high-profile investors and board members, Theranos raised hundreds of millions of dollars on the promise of miniaturised blood-testing devices that could run hundreds of tests. This book is a paperback edition published by Picador, suitable for adult readers (18+).4,99 £*Shipping: 2,99 £Secure redirect to the provider


-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
Top-Angebote
Products related to Tpm:
-
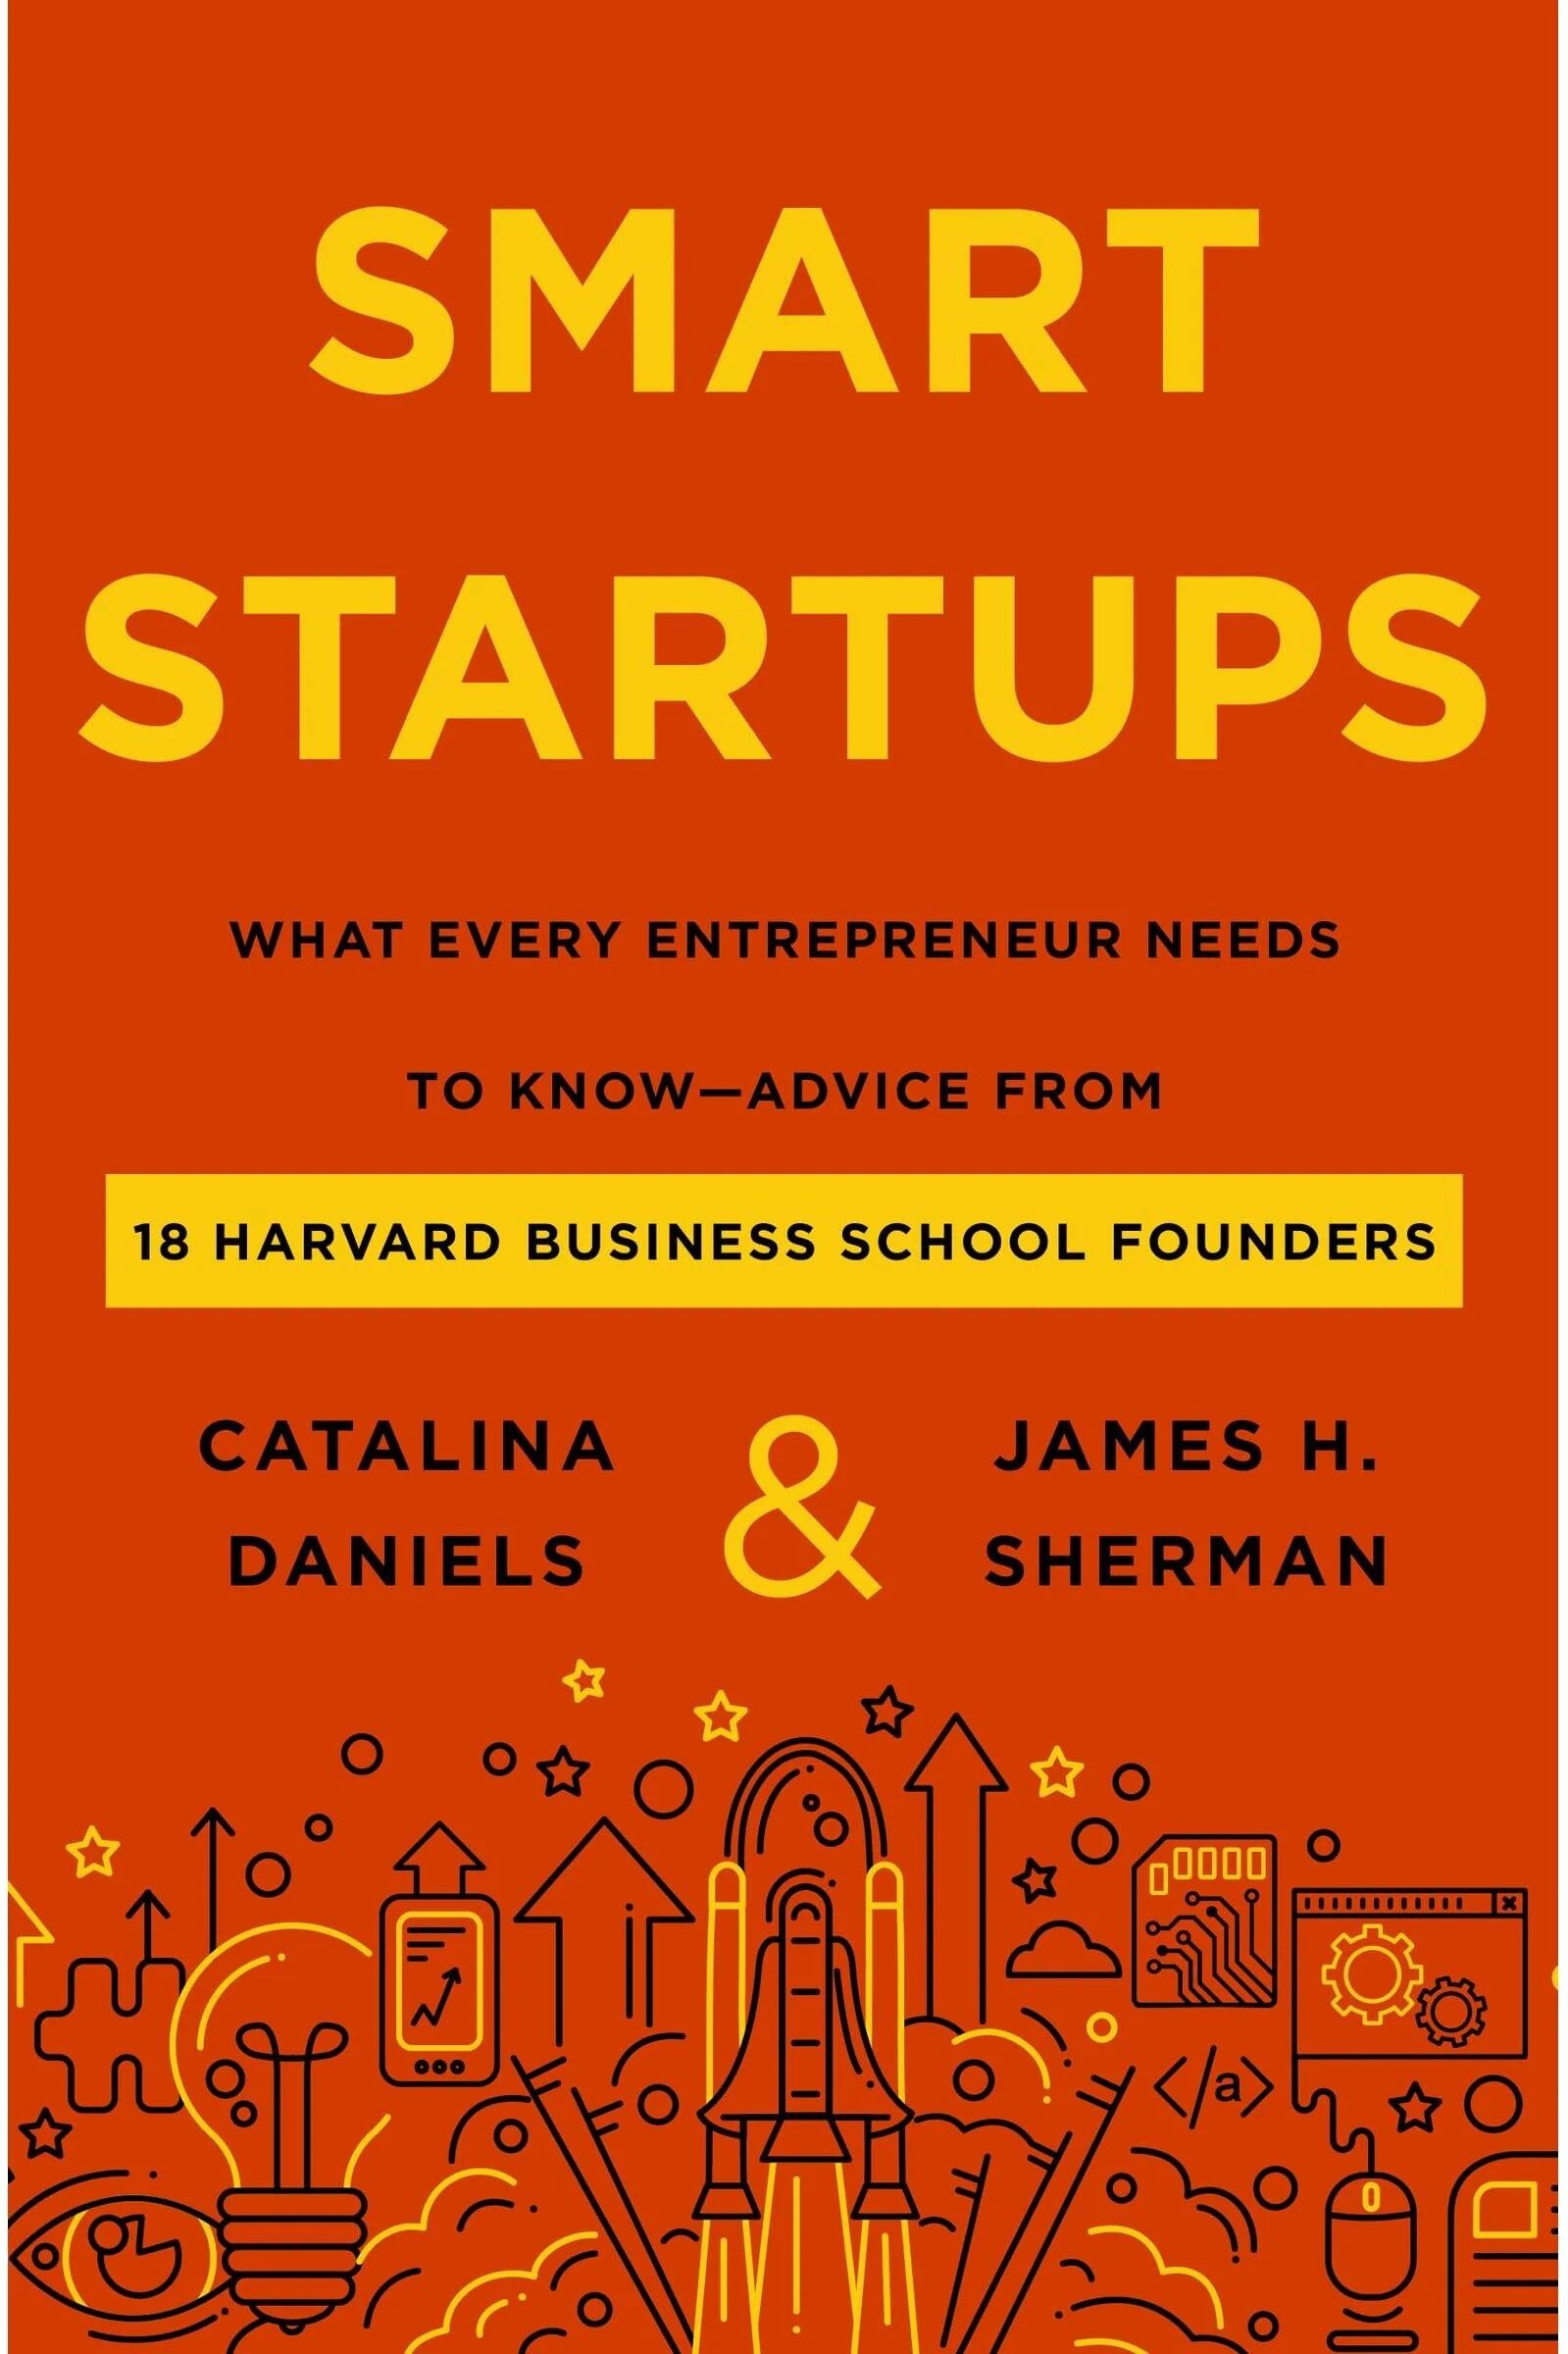
Harper Business Smart Startups: What Every Entrepreneur Needs to Know by Catalina Daniels & James H. Sherman - Hardback - Business & Entrepreneurship Non FictionSmart Startups: What Every Entrepreneur Needs to Know is a candid guide to building a company that lasts. Written by two Harvard Business School classmates turned founders and angel investors, it goes beyond classroom theory to show what actually happens inside eighteen startups launched by fellow HBS graduates. Packed with honest case studies, hard-won lessons, and unexpected pitfalls, this book is essential reading for anyone serious about turning an idea into a viable business. The authors, Catalina Daniels and James H. Sherman, met as classmates at Harvard Business School, where they studied the fundamentals of entrepreneurship together. Years later, after each had founded and exited multiple companies and become active angel investors, they discovered that their real-world experiences often diverged sharply from the conventional wisdom they learned in school.11,99 £*Shipping: 2,99 £Secure redirect to the provider
-
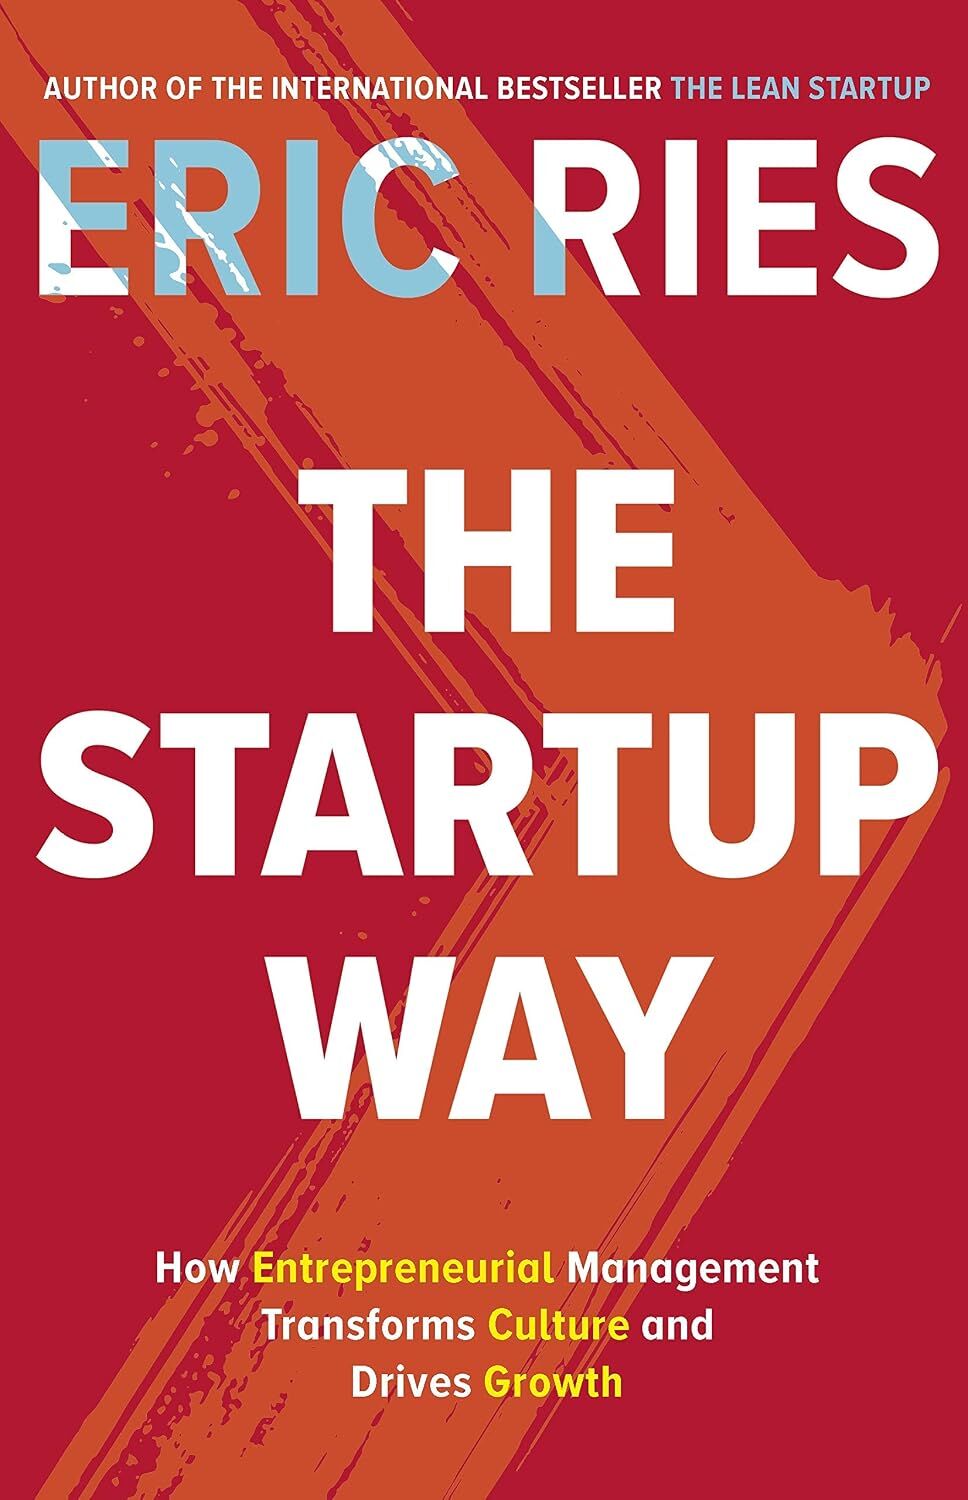
Portfolio Penguin Eric Ries Collection 2 Books Set - The Lean Startup & The Startup Way - Paperback - Business & Entrepreneurship Bundle for Founders and ManagersThis two-book collection brings together Eric Ries's most influential works on modern entrepreneurship: The Lean Startup and The Startup Way. Together they set out a rigorous, practical methodology for building successful businesses in conditions of extreme uncertainty, then show how those same lean principles can be scaled up to transform established, bureaucratic organisations. The Lean Startup introduced the world to concepts such as the minimum viable product, validated learning, and the build-measure-learn feedback loop. Drawing on his own experiences as a founder and advisor, Ries argues that startups succeed not through grand five-year plans but through rapid experimentation and continuous improvement. Ideal for founders, managers, and anyone curious about innovation, this set is a complete primer on lean thinking from the man who coined the term. The books are in brand new condition, published by Portfolio Penguin, and are suitable for adult readers.10,99 £*Shipping: 2,99 £Secure redirect to the provider
-
Flythe Consulting Arika Wall Sconce Pair, Pair, Satin NickelThe Arika Wall Sconce Pair is an adaptation of old-fashioned light fixtures, with an appealing design that will complement modern decor. The lacquered solid brass sconces have 4.75 dia.x7 H clear glass hurricanes that will protect your standard...179,00 $*Shipping: 22,95 $Secure redirect to the provider
-
Why does the PC crash during startup? TPM 2.0
The PC may crash during startup due to issues with the Trusted Platform Module (TPM) 2.0. TPM 2.0 is a hardware-based security feature that stores encryption keys, passwords, and digital certificates. If there are compatibility issues with the TPM 2.0 chip or its firmware, it can cause the PC to crash during startup. Additionally, if the TPM 2.0 is not properly initialized or configured, it can also lead to startup crashes. It is important to ensure that the PC's hardware and firmware are compatible with TPM 2.0 and that it is properly set up to avoid startup crashes. **
-
What is BitLocker TPM?
BitLocker TPM (Trusted Platform Module) is a security feature in Windows operating systems that uses a hardware component called TPM to provide enhanced protection for data stored on a computer's hard drive. TPM is a microchip that securely stores encryption keys, passwords, and other sensitive information to help protect against unauthorized access to the system. When BitLocker TPM is enabled, the encryption keys are securely stored in the TPM, making it more difficult for attackers to access the data even if they physically remove the hard drive from the computer. **
-
Can't you activate TPM?
Yes, TPM (Trusted Platform Module) can be activated on compatible devices through the device's BIOS settings. However, not all devices have TPM built-in, so it's important to check the device's specifications to see if TPM is available. Once activated, TPM provides hardware-based security features such as secure boot, device encryption, and key management to help protect sensitive data and ensure the integrity of the system. **
-
What exactly is TPM 2.0?
TPM 2.0, which stands for Trusted Platform Module 2.0, is a hardware-based security feature that provides a secure foundation for various security functions, such as encryption, authentication, and key management. It is a microcontroller that is typically integrated into computer systems to enhance security by securely storing sensitive information, such as encryption keys, digital certificates, and passwords. TPM 2.0 helps protect against various security threats, including unauthorized access, malware attacks, and data breaches, by providing a secure environment for sensitive data and cryptographic operations. **
Similar search terms for Tpm
-
Flythe Consulting Jonetia Hurricane Wall Sconce Pair Satin Brass, Pair, Satin BrassThe Jonetia Satin Brass Hurricane Wall Sconce Pair proudly displays grandeur on your walls. These hand-forged, solid brass sconces feature a diamond design and fleur-de-lis motif. Sconces have a lacquered, satin brass finish that is done by hand. A...229,00 $*Shipping: 32,06 $Secure redirect to the provider
-
Picador Bad Blood: Secrets and Lies in a Silicon Valley Startup by John Carreyrou - Paperback - True Crime Business Book - Theranos Scandal ExposéBad Blood is John Carreyrou's Pulitzer Prize-winning investigation into Theranos, the blood-testing startup once valued at over $9 billion before collapsing into one of the biggest corporate frauds in American history. This gripping true-crime business narrative follows founder Elizabeth Holmes from Silicon Valley darling to disgraced fraudster, exposing the culture of secrecy, intimidation, and deception that hid a technology which simply didn't work — with devastating consequences for real patients. In 2014, Elizabeth Holmes was celebrated as the next Steve Jobs: a charismatic Stanford dropout whose startup promised to revolutionise healthcare with a single drop of blood. Backed by high-profile investors and board members, Theranos raised hundreds of millions of dollars on the promise of miniaturised blood-testing devices that could run hundreds of tests. This book is a paperback edition published by Picador, suitable for adult readers (18+).4,99 £*Shipping: 2,99 £Secure redirect to the provider
-
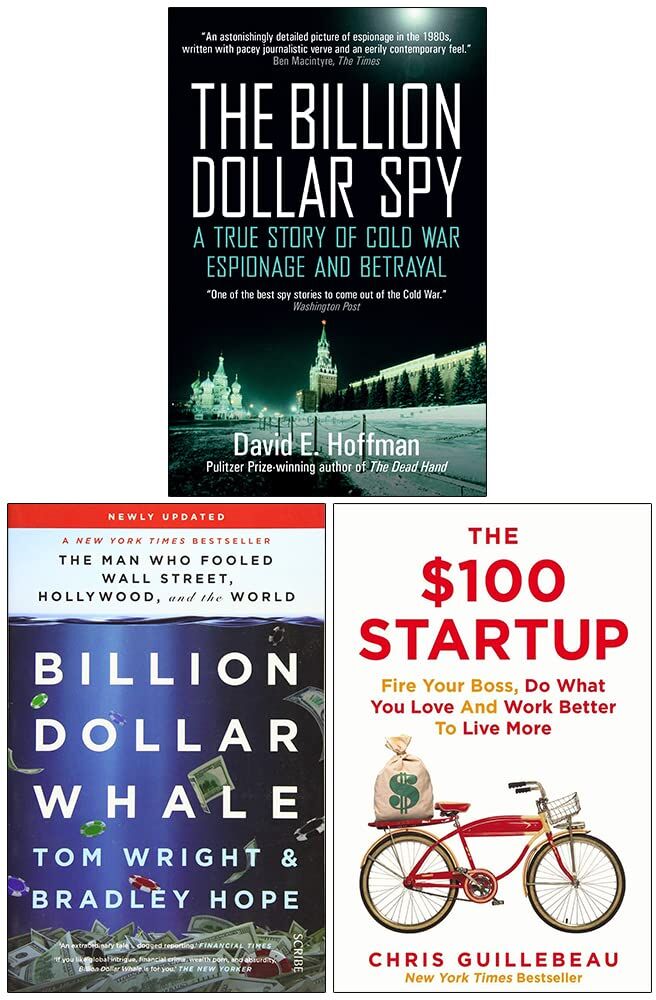
Various Publishers Billion Dollar Spy, Billion Dollar Whale, The $100 Startup - 3 Books Collection Set - Paperback - True Crime, Finance & Business Non-Fiction Gift SetThis three-book non-fiction collection includes The Billion Dollar Spy by David E. Hoffman, Billion Dollar Whale by Tom Wright and Bradley Hope, and The $100 Startup by Chris Guillebeau. The books offer gripping true stories of espionage and financial fraud, alongside practical entrepreneurship advice. The Billion Dollar Spy uncovers Cold War spy-craft in Moscow, Billion Dollar Whale exposes one of history's largest financial scandals, and The $100 Startup delivers a hands-on blueprint for building a business from scratch. The books are in new condition, published by Icon Books, Scribe UK, and Pan Macmillan, and are suitable for adult readers.13,99 £*Shipping: 2,99 £Secure redirect to the provider
-
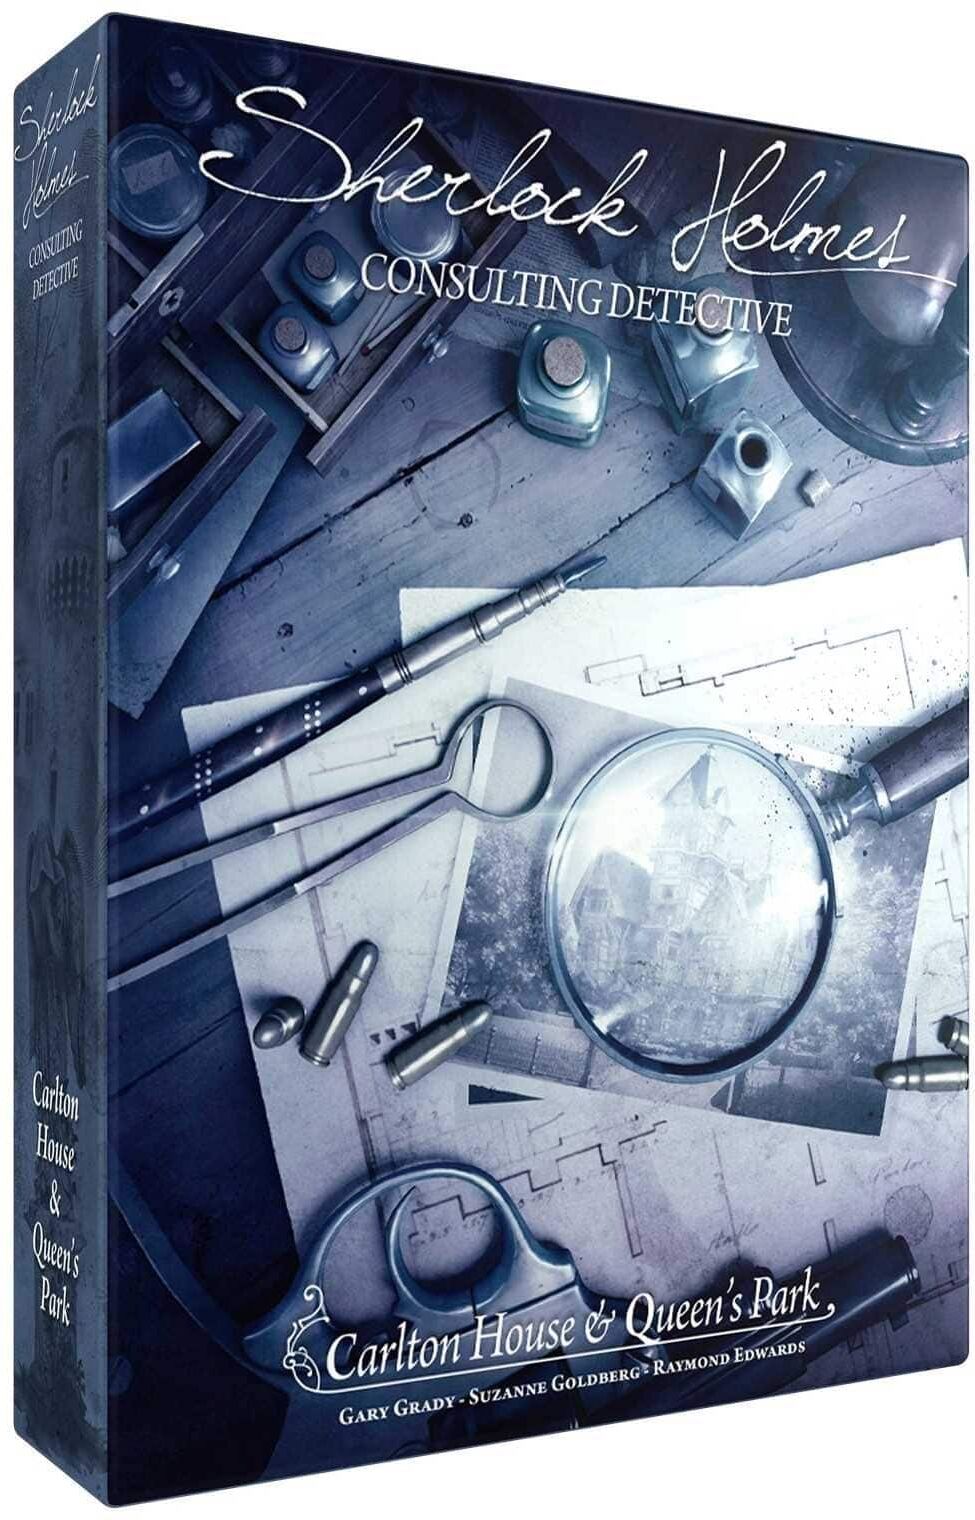
Space Cowboys Sherlock Holmes Consulting Detective - Carlton House & Queen's Park Board Game - 10 CasesStep into Victorian London and investigate a new collection of challenging cases in this standalone edition of Sherlock Holmes: Consulting Detective. Includes 10 cases with varying levels of difficulty for immersive group play.26,79 £*Shipping: 3,95 £Secure redirect to the provider
-
How do I activate TPM?
To activate TPM (Trusted Platform Module) on your computer, you will need to access the BIOS or UEFI settings. Restart your computer and enter the BIOS/UEFI by pressing a specific key (usually F2, F10, or Del) during the boot-up process. Look for the TPM settings in the security or advanced settings section and enable TPM. Save the changes and exit the BIOS/UEFI settings. TPM should now be activated on your computer. **
-
How can one delete TPM?
To delete TPM (Trusted Platform Module) on a computer, you would need to access the computer's BIOS or UEFI settings. Once in the settings, you can navigate to the security or TPM section and find the option to clear or reset the TPM. This will remove any existing TPM data and settings from the computer. It's important to note that deleting TPM may have implications for the computer's security and functionality, so it should only be done if necessary and with caution. **
-
Does it support TPM 2.0?
Yes, the device supports TPM 2.0. TPM (Trusted Platform Module) 2.0 is a security feature that provides hardware-based security functions, such as cryptographic keys and secure boot, to help protect the device from unauthorized access and tampering. This ensures that the device has a secure foundation for running trusted applications and protecting sensitive data. **
-
How can I update TPM?
To update TPM (Trusted Platform Module), you can follow these steps: 1. Check for TPM firmware updates on the manufacturer's website or through the device's management software. 2. Download the latest TPM firmware update and follow the instructions provided by the manufacturer for installation. 3. Ensure that your device is connected to a stable power source and that all other applications are closed during the update process. 4. Restart your device after the update is complete to ensure that the changes take effect. It's important to regularly check for TPM updates to ensure that your device has the latest security features and bug fixes. **
* All prices are inclusive of VAT and, if applicable, plus shipping costs. The offer information is based on the details provided by the respective shop and is updated through automated processes. Real-time updates do not occur, so deviations can occur in individual cases. ** Note: Parts of this content were created by AI.